DevOps Engineering in the Age of Autonomous Agents: Principles and Convictions
Sun 08 November 2026
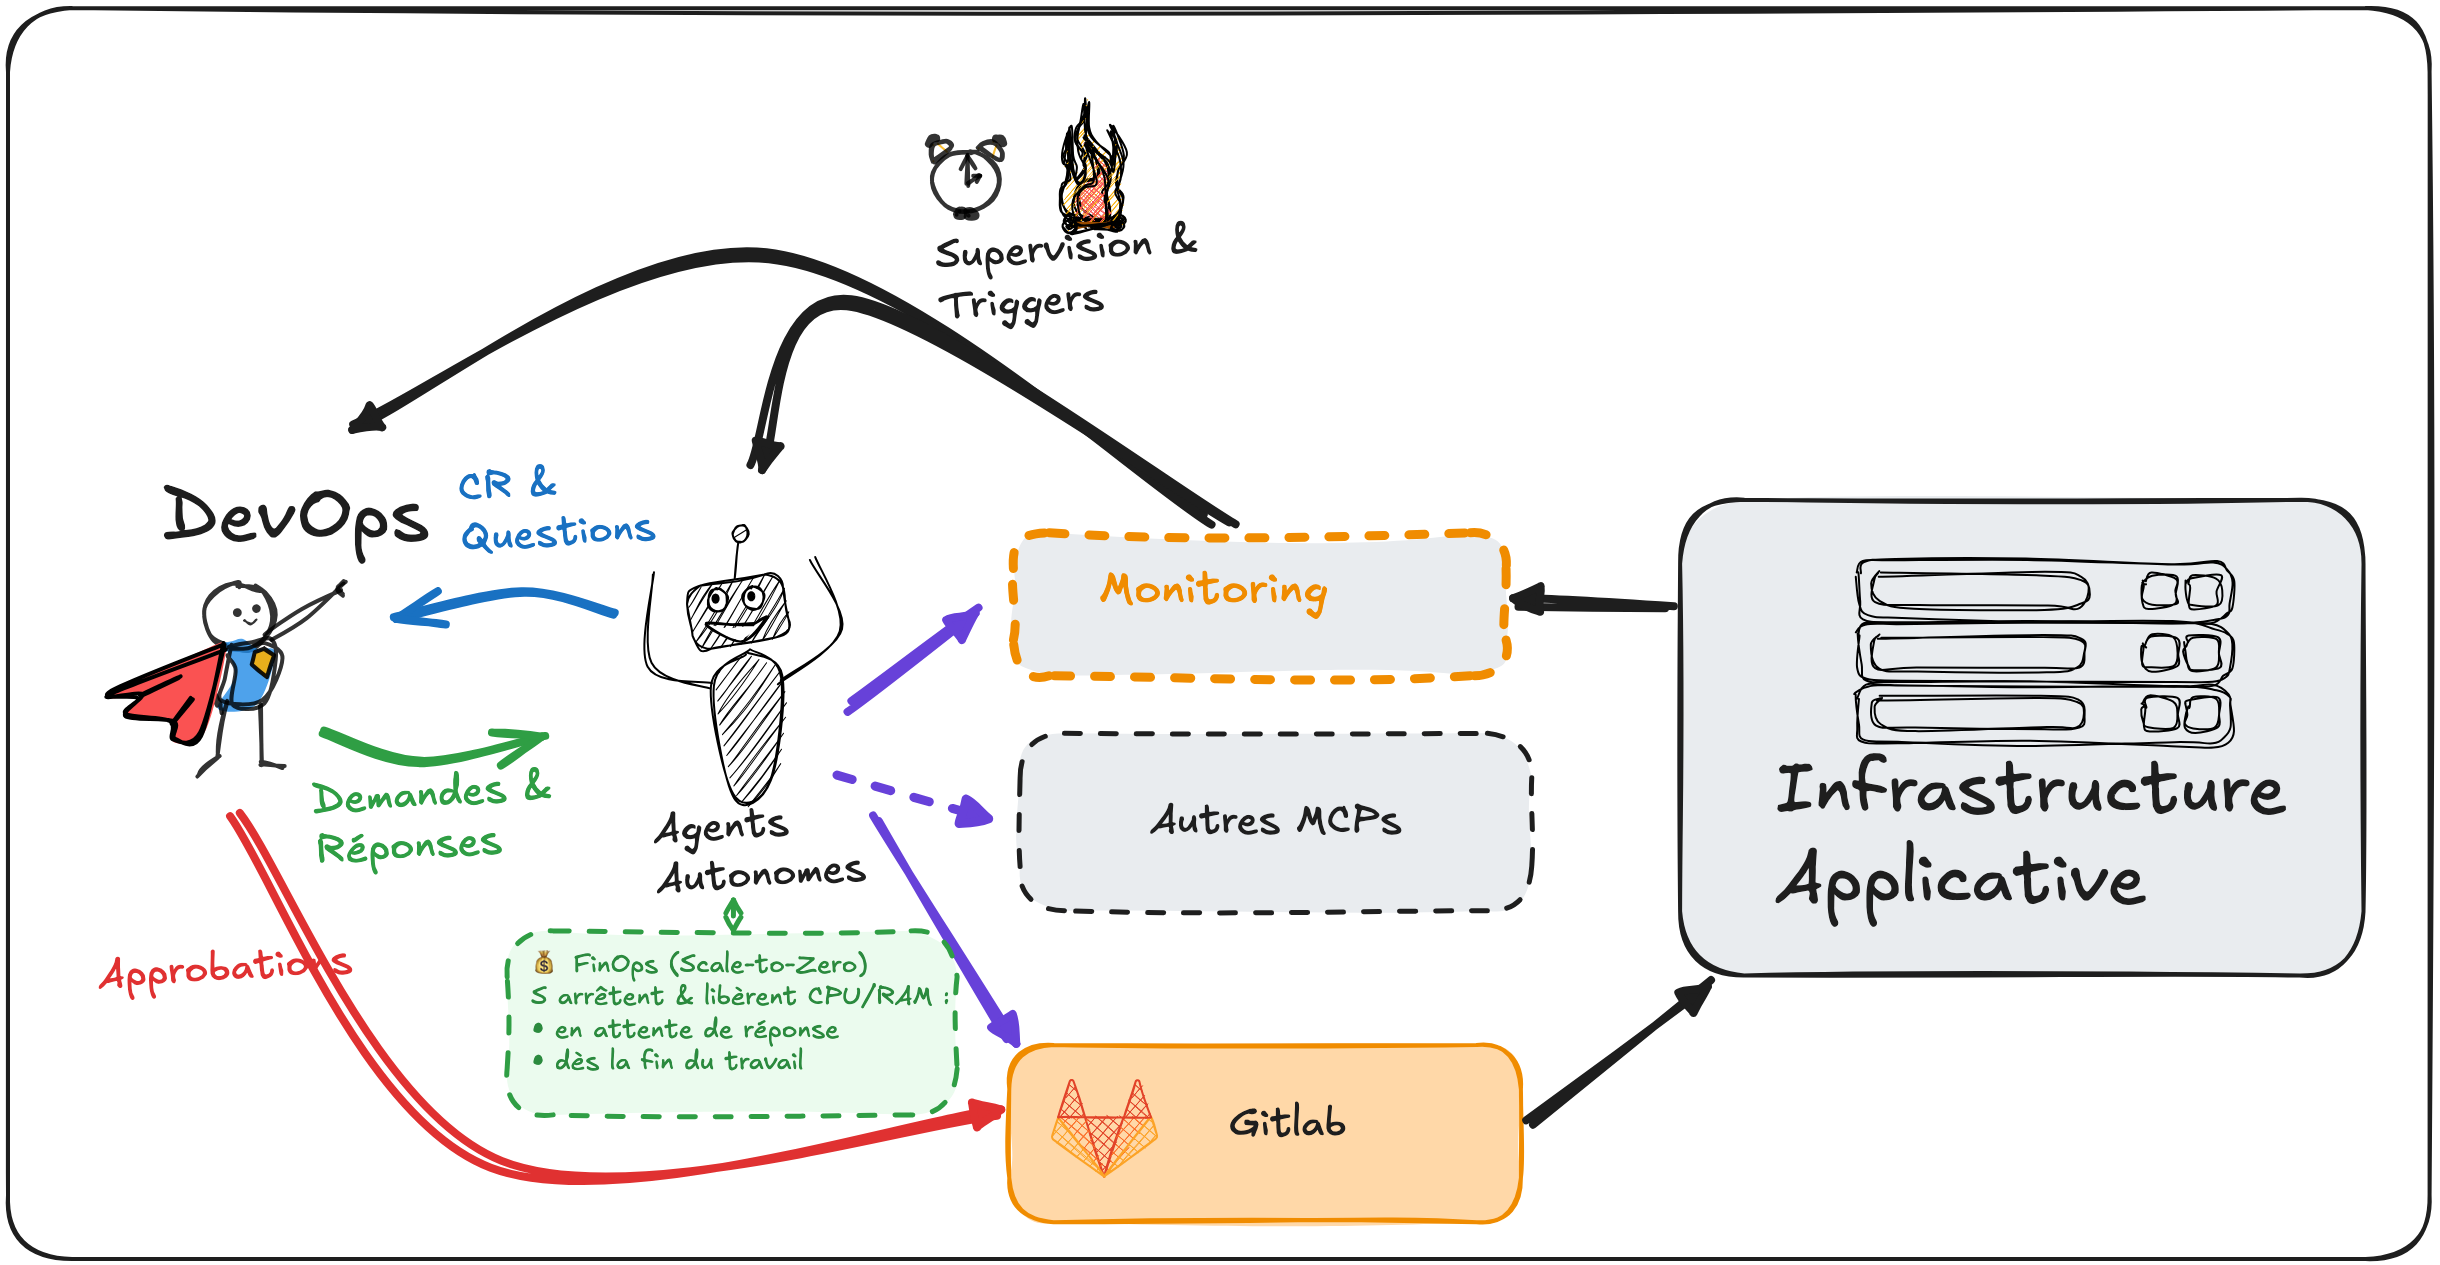
Principles, convictions, and architecture requirements for building a trusted autonomous agent platform in DevOps engineering.
Continue reading » Cloud Ops Chronicles
Just another devops lover
Principles, convictions, and architecture requirements for building a trusted autonomous agent platform in DevOps engineering.
Continue reading »
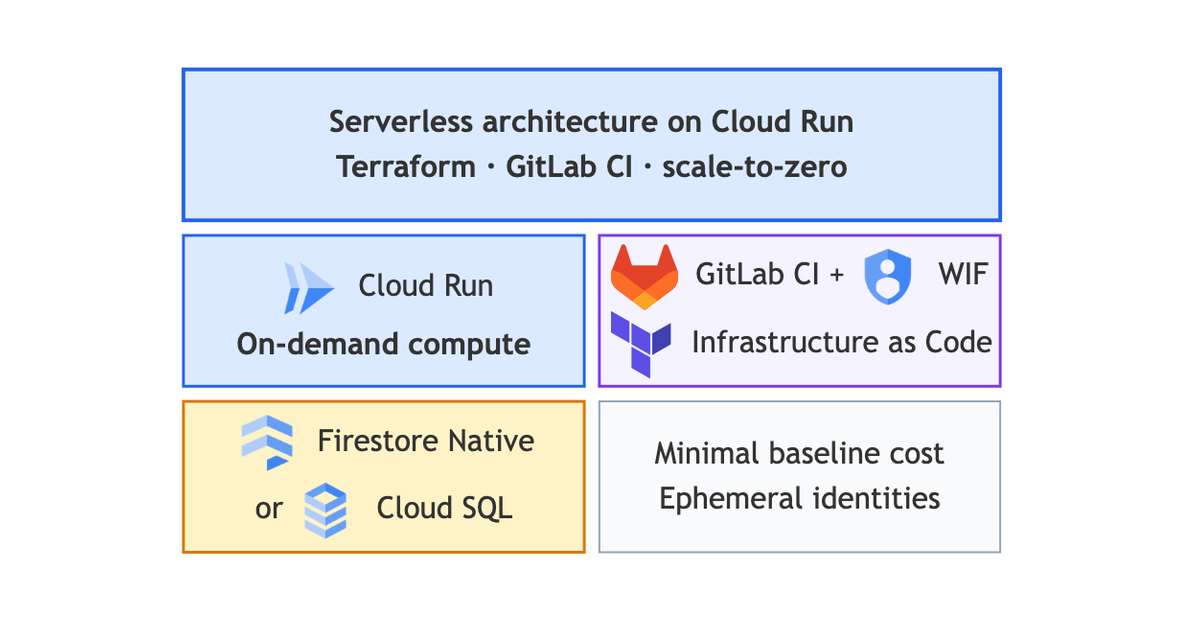
A practical Cloud Run stack for intermittent workloads: Firestore, Cloud SQL or GCS Volume Mounts, Terraform, and keyless GitLab CI through Workload Identity Federation.
Continue reading »

“Supprimez les clés JSON de Service Account en les remplaçant par une authentification matérielle TPM/Secure Enclave via GCP Workload Identity Federation.”
Continue reading »
“Remove static Service Account JSON keys by replacing them with hardware-based TPM/Secure Enclave authentication using GCP Workload Identity Federation.”
Continue reading »
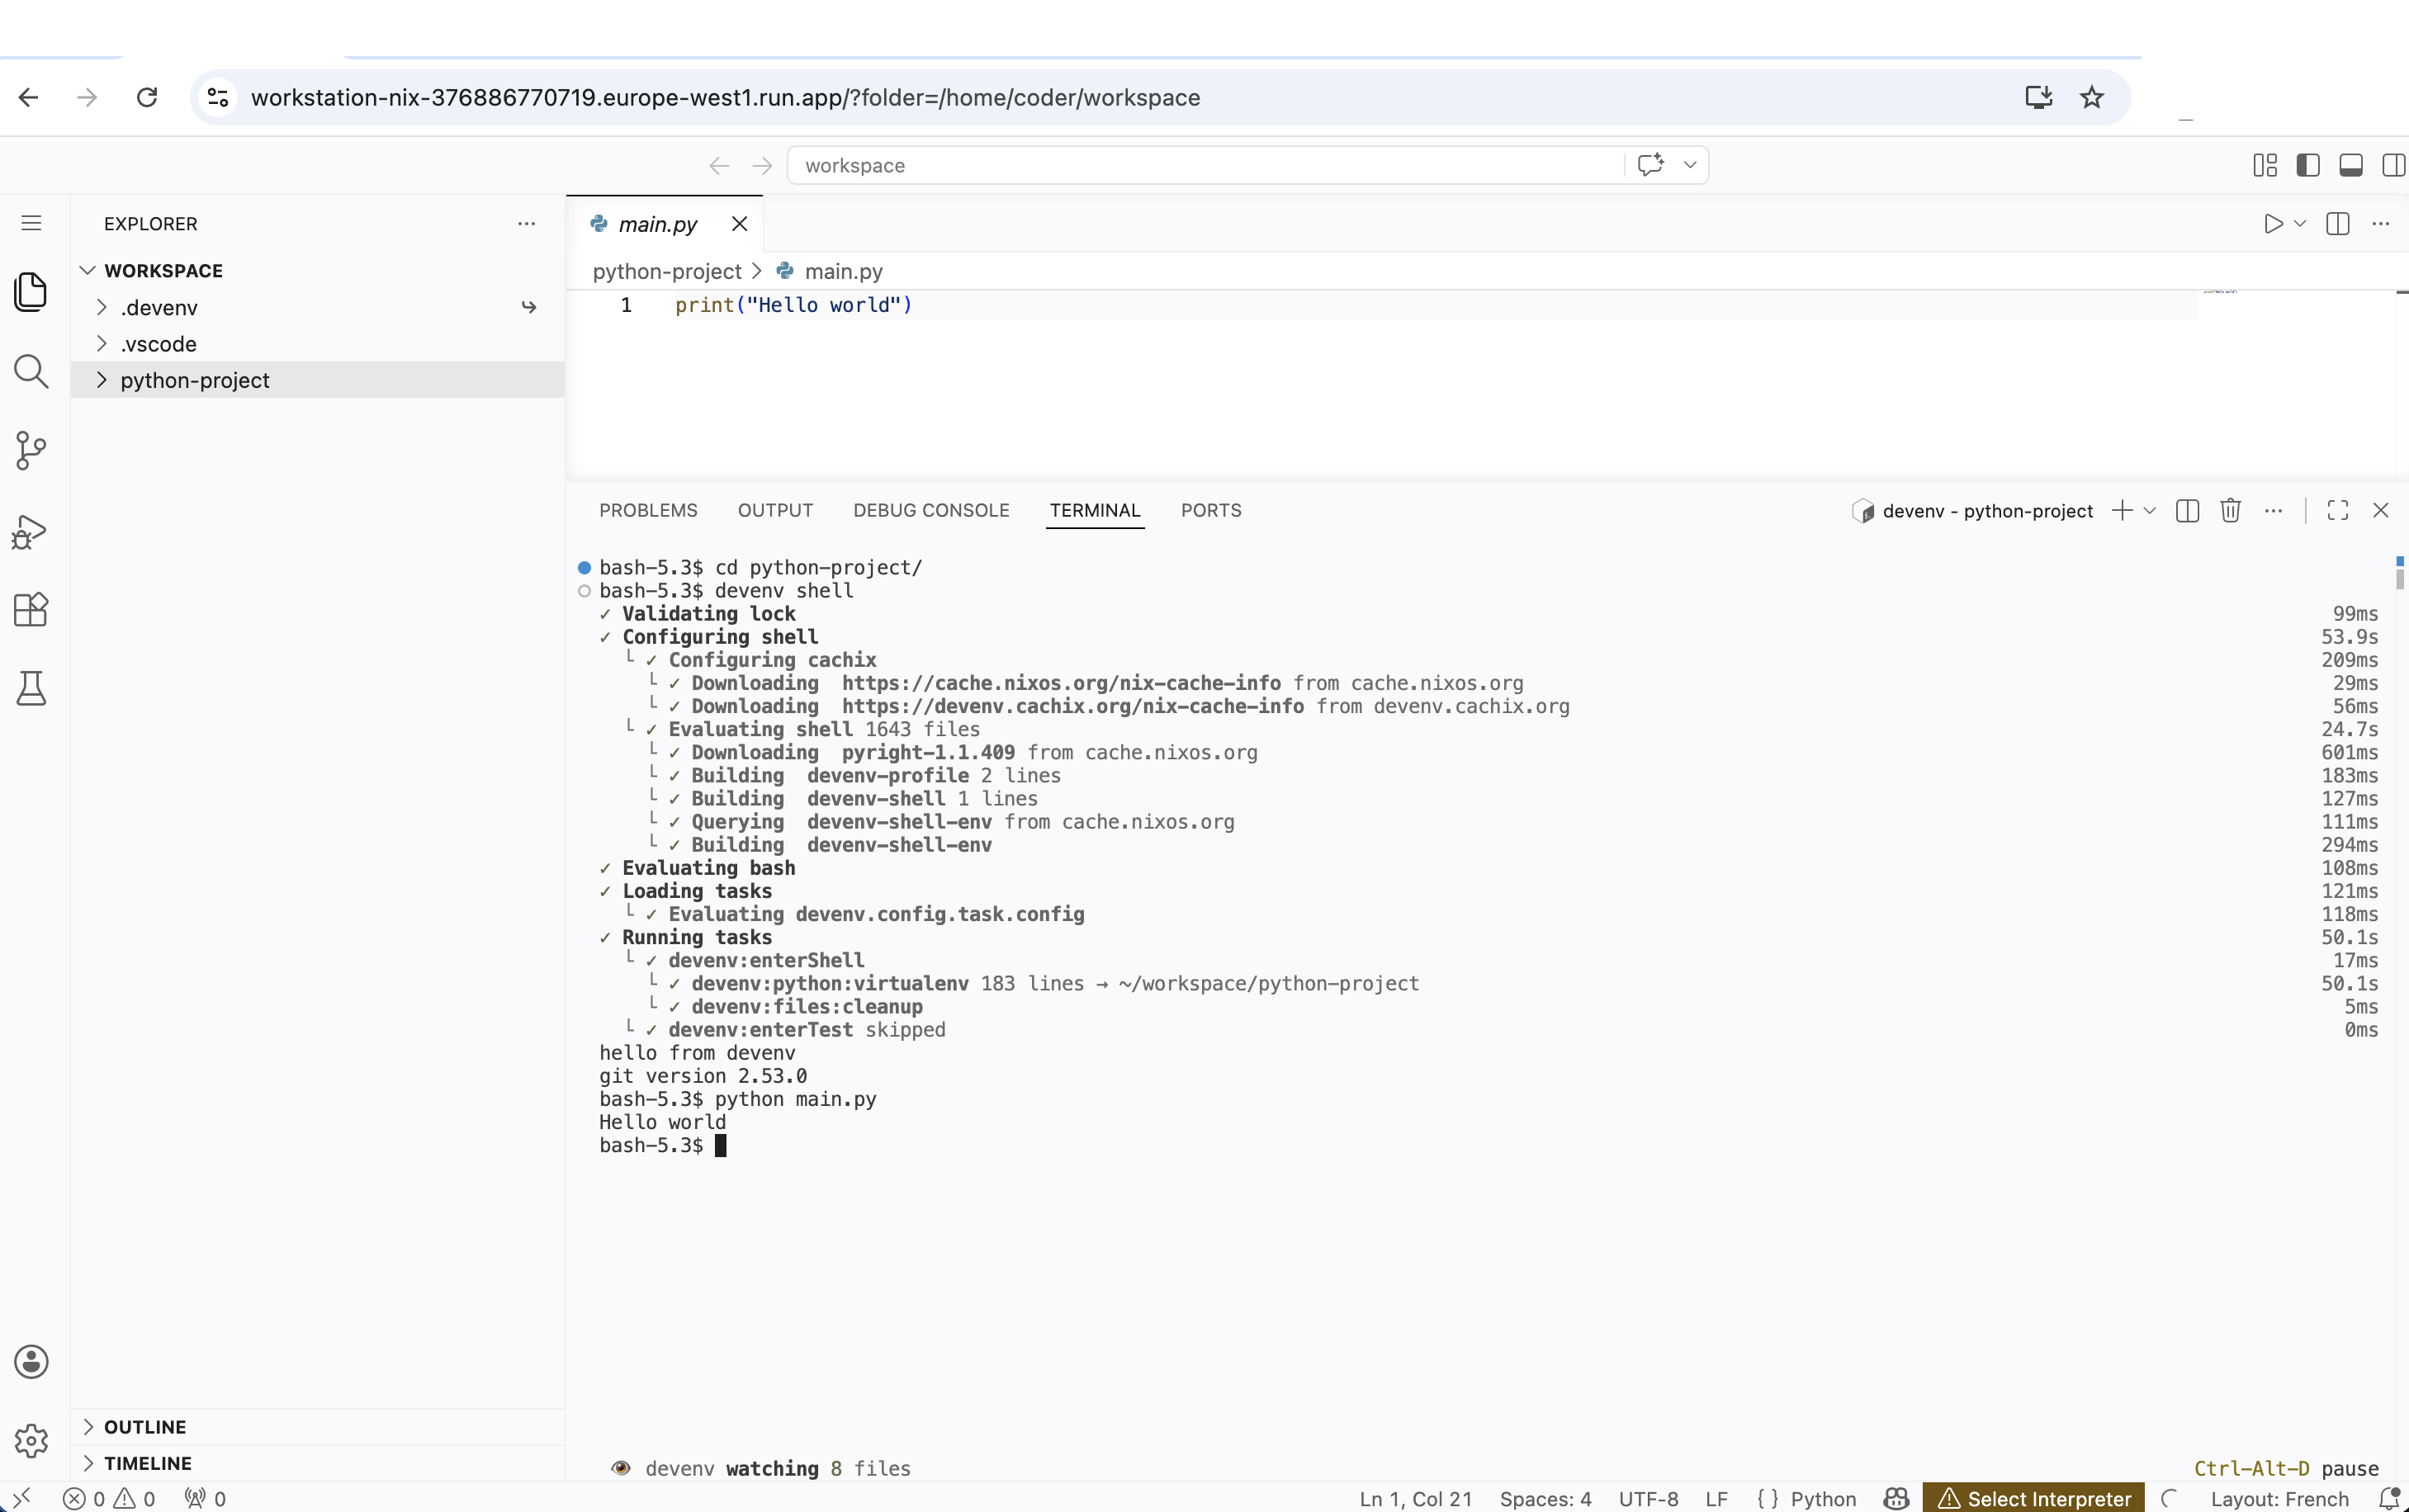
A reproducible VS Code Workstation on Cloud Run, powered by Nix, designed for Human-AI collaboration loops — with a $0.00 idle cost.
Continue reading »

How I used Gemini 3, Vertex AI, and Cloud Run to transform Google Cloud release notes into an engaging weekly podcast. Detailed architecture and code.
Continue reading »

Leveraging Google Cloud Platform’s Platform-as-a-Service (PaaS) capabilities, you can effortlessly deploy and manage your HashiCorp Vault instance
Continue reading »